Security Simplified: A Pragmatic Approach
Summary
This blog post, "Security Simplified: A Pragmatic Approach", is a blueAPACHE article from 2017 covering security. Last week, bueAPACHE hosted our Insight Event luncheon in Melbourne. blueAPACHE Insight Events are an intimate affair limited to a single table and offer a unique opportunity to interact with a leading industry expert, ask questions, gain insights and discuss the challenges that organisations face. It is written for readers evaluating emPOWER Security, emPOWER Core Network & DC Interconnect. The underlying security practice it describes, reducing attack surface and improving detection and response, is not tied to a specific product version and remains relevant to any organisation managing cyber risk today.
Key facts
| Label | Value |
|---|---|
| Publication year | 2017 |
| Topic | Security Simplified: A Pragmatic Approach |
| Services referenced | emPOWER Security, emPOWER Core Network & DC Interconnect |
| Named products or vendors | None named beyond blueAPACHE |
Article
Last week, bueAPACHE hosted our Insight Event luncheon in Melbourne. blueAPACHE Insight Events are an intimate affair limited to a single table and offer a unique opportunity to interact with a leading industry expert, ask questions, gain insights and discuss the challenges that organisations face. Bill Robson, Security Practice Lead at blueAPACHE, has been engaged in information security for over 20 years. Having held senior roles as an information security consultant and penetration tester for global organisations such PricewaterhouseCoopers and Deloitte, he is regarded as a leading expert in his field. His deep technical knowledge and vast experience is complimented by a passion for simplifying IT security. The discussion, over some really good wine and steak, focussed on how technology threats can translate into business risks and a pragmatic way for organisations to assess and combat that risk. For many organisations today, cybersecurity is a beast that is too complex, too expensive and too challenging to stay ahead of.
“What I’ve observed is that often there is a disconnect between technologists and key decision makers within organisations”, said Bill. “While security experts tend to worry about the nitty-gritty of day to day running of their networks and systems, they often miss the commercial reality of doing business. The answer lies in using the language of risk to communicate.” Key aspects of Bill’s pragmatic approach to security include:
- Information security is not the sole responsibility of the IT team. In order for your security measures to be successful, every business unit needs to be involved in the conversation regarding what constitutes a risk and the cost of combating it.
- There is no need to reinvent the wheel. Identify and utilise industry standard compliance tools and best practises.
- Use an information security risk register to drive the security agenda and make use of smart tools, not spreadsheets, to manage your risk register.
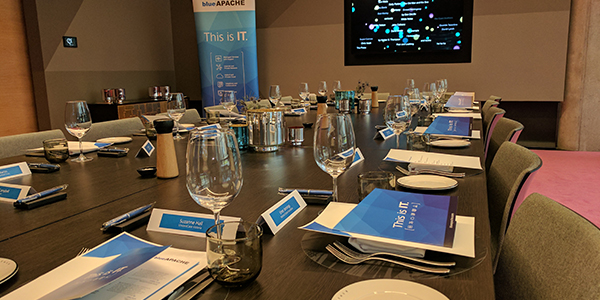
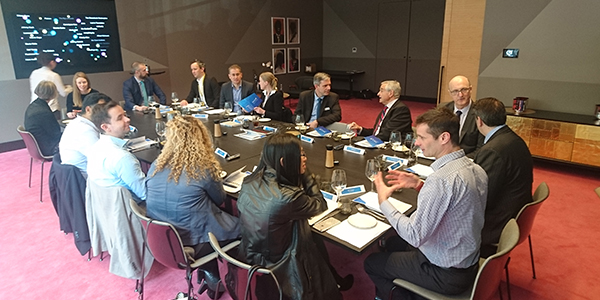
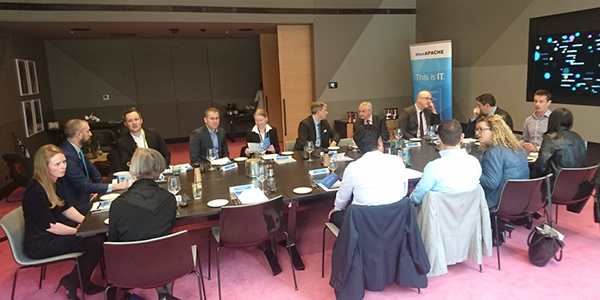
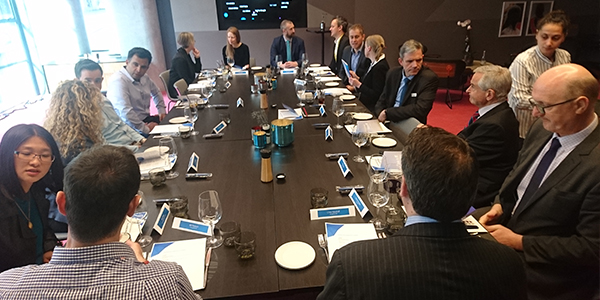
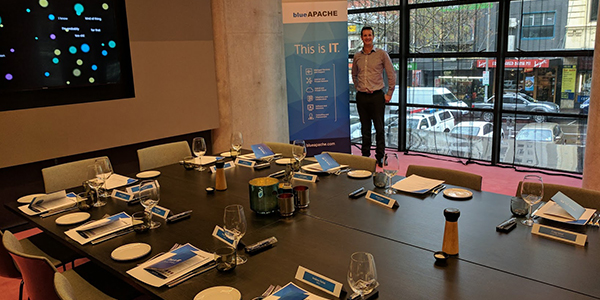 blueAPACHE would like to thank all those who attended. If you would like to be invited to future blueAPACHE Insight Events, you can register your interest here.
To learn more about blueAPACHE’s complete security offering, contact our security team.
Related
- emPOWER Security
- emPOWER Security (pillar hub)
- emPOWER Core Network & DC Interconnect
- emPOWER Connectivity (pillar hub)
Frequently asked questions
Who is Bill Robson, and what is his professional background according to this post?
Bill Robson is blueAPACHE's Security Practice Lead, with more than 20 years in information security, including senior roles as an information security consultant and penetration tester for global organisations such as PricewaterhouseCoopers and Deloitte.
What kind of event does this post describe, and what format does it take?
The post describes a blueAPACHE Insight Event luncheon held in Melbourne, which it says is an intimate affair limited to a single table, offering attendees the chance to interact directly with a leading industry expert over food and wine.
What disconnect did Bill Robson say he has observed between technologists and business decision-makers?
Bill Robson said he has observed a disconnect where security experts focus on the day-to-day running of networks and systems but often miss the commercial reality of doing business, and that the answer lies in using the language of risk to communicate with decision-makers.
Does Bill Robson say information security should be the IT team's sole responsibility?
No. He said information security is not the sole responsibility of the IT team, and that for security measures to succeed, every business unit needs to be involved in the conversation about what constitutes a risk and the cost of combating it.
What does Bill Robson recommend regarding compliance tools and best practice?
He said there is no need to reinvent the wheel, and organisations should identify and use industry standard compliance tools and best practices rather than building their own from scratch.
What does Bill Robson recommend for managing an organisation's security risk register?
He recommends using an information security risk register to drive the security agenda, and using purpose-built smart tools rather than spreadsheets to manage that risk register.
Where was this particular blueAPACHE Insight Event held, and what was discussed?
The post says this Insight Event luncheon was held in Melbourne, with the discussion, held over wine and steak, focused on how technology threats translate into business risks and a pragmatic way for organisations to assess and combat that risk.
How does the post describe the challenge cybersecurity presents to many organisations today?
The post says that for many organisations today, cybersecurity is a beast that is too complex, too expensive and too challenging to stay ahead of.
Source
- origin post (2017)
Knowledge Base
What is the blog post 'Security Simplified: A Pragmatic Approach' about?
The blog post recaps a blueAPACHE Insight Event luncheon held in Melbourne, where Bill Robson, Security Practice Lead at blueAPACHE, discussed how technology threats translate into business risks and outlined a pragmatic way for organisations to assess and combat that risk.
Who is Bill Robson and what is his background?
Bill Robson is the Security Practice Lead at blueAPACHE who has been engaged in information security for over 20 years. He previously held senior roles as an information security consultant and penetration tester for global organisations such as PricewaterhouseCoopers and Deloitte, and is regarded as a leading expert in his field.
What are blueAPACHE Insight Events?
blueAPACHE Insight Events are intimate luncheon events limited to a single table that offer attendees a unique opportunity to interact with a leading industry expert, ask questions, gain insights, and discuss challenges organisations face.
According to Bill Robson, what disconnect often exists within organisations regarding security?
Bill Robson observed that there is often a disconnect between technologists and key decision makers within organisations — security experts tend to focus on the day-to-day running of networks and systems and often miss the commercial reality of doing business. He suggests the answer lies in using the language of risk to communicate.
What are the key aspects of Bill Robson's pragmatic approach to security?
The key aspects are: (1) information security is not the sole responsibility of the IT team and every business unit needs to be involved in conversations about risk and cost; (2) there is no need to reinvent the wheel — organisations should identify and utilise industry standard compliance tools and best practices; and (3) organisations should use an information security risk register to drive the security agenda, employing smart tools rather than spreadsheets to manage the risk register.
When was this blog post originally published?
The blog post was written by blueAPACHE and dated July 26, 2017, with a read time of 2 minutes.
How can someone register interest in future blueAPACHE Insight Events?
Readers who want to be invited to future blueAPACHE Insight Events can register their interest via the contact page linked in the article (blueapache.com/contact).
How can someone learn more about blueAPACHE's security offering?
The article directs readers to contact blueAPACHE's security team, via the contact page, to learn more about blueAPACHE's complete security offering.
Images on This Page
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a6ffec7d87be5a881637bba_31b5a84971e1d1ce71dc99ca059bfbde_blueAPACHE.svg
blueAPACHE logo on a dark blue background
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bdfb153d68a8eeb6ac2_Insight-Event.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a713402a5a7f7ebf553f0bf_Background-Top.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701be1b153d68a8eeb6b7a_IE1.jpeg
blueAPACHE Insight event
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701be1b153d68a8eeb6b77_IE1a.jpeg
blueAPACHE Insight event
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701be1b153d68a8eeb6b67_IE2.jpeg
blueAPACHE Insight event
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701be1b153d68a8eeb6b86_IE-2.jpeg
blueAPACHE Insight event
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701be1b153d68a8eeb6b90_IE-5.jpeg
blueAPACHE Insight event
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701b59b153d68a8eeb0e36_BBanner-1-Windows-10-is-out.-AI-is-in.-.avif
You’ve Invest in Security. So Why Are Breaches Still Happening?
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb807b7741bf53e298a_BBanner-1-Windows-10-is-out.-AI-is-in.-8.avif
EOFY 2026: The Reset Is Done – Now It’s About Getting Ahead
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d0_BBanner-2-When-support-ends-risk-begins-4.avif
Why Every Business Needs AI Guardrails
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d7_BBanner-2-When-support-ends-risk-begins-3.avif
Ransomware Incident Response: Why Paying the Ransom Is a Failure of Preparation
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb707b7741bf53e297d_BBanner-2-When-support-ends-risk-begins-1.avif
The 7 Cyber Truths Boards Must Act On In 2026
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29f9_BBanner-1-Windows-10-is-out.-AI-is-in.-7.avif
Reflecting on an Outstanding 2025 – Thank You for Your Partnership
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e2a0c_Procurement-Portal.avif
The blueAPACHE e-Store: IT purchasing made simple
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29ec_BBanner-1-Windows-10-is-out.-AI-is-in.-5.avif
Building Our Cyber Safe Culture: A Practical Guide for CSAM 2025
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fbfad31fa678fefd51a_6a704f395a0a01b8e482853a_support-monitor.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4563e_6a704f3a400fc8e661400519_support-user.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45639_6a704f3a91ffd7d0dbc40847_support-phone.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4562f_6a704f3747d60bd3f65b7a31_support-globe.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45636_6a704f38eb60992797acf5d9_support-mail.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45633_6a704f3a07b7741bf54f2122_support-speech-bubble.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a707520ca872d1b5a69a518_Sensiba.avif
Sensiba ISO/IEC 27001 Certified badge with a diamond-shaped logo below the text.